Tag: ansible

  • Ansible with DellEMC Storage: Part 3 – Installing DellEMC PowerMax Ansible Module

    Ansible with DellEMC Storage: Part 3 – Installing DellEMC PowerMax Ansible Module

    This blog is the continuation of Ansible with DellEMC storage multi-part blog. 

    In Part 1 of this series, we discussed getting started with the installation of dependencies for the Ansible and DellEMC Ansible module, followed by Ansible installation.

    In Part 2 we discussed the high-level basics of Ansible to get you started quickly.

    The purpose of earlier blogs was to get you to familiarize yourself with Ansible. In this blog, we will talk about DellEMC PowerMax Ansible module.

    First let’s get our management server ready. Make sure following pre-requisites are in place

    • PowerMax is running with Unisphere 9.0
    • Red Hat Enterprise Linux 7.5 (or equivalent). CentOS in my case
    • Ansible is installed (min version 2.6)
    • Python 2.7.12 or higher is installed
    • Python library for Unisphere (PyU4V) 3.0.0.14 is installed

    Ansible relies on Python and the Ansible for PowerMax modules rely on the PyU4V Python library. Check this link for more details on the latest PyU4V module.

    Make sure that Python and ā€œpipā€ are installed. pip is a Python package manager. Install ā€œpipā€ if required and then use it to install PyU4V.

    Below commands will get pip and PyU4V installed.

    # python -V
    # pip -V
    # yum install python-pip
    # pip install PyU4V

    Once the system is ready with required packages next step is to get the PowerMax module from GitHub. To get the modules run below commands.

    # git clone https://github.com/dell/ansible-powermax
    # cd dellemc_ansible
    # ls

    This folder (dellemc_ansible) contains multiple documents including ā€œProduct Guideā€ and ā€œRelease Notesā€ for the downloaded version.

    We also need to copy a few files from downloaded modules to Ansible directories. Follow below process to complete the copy operation

    # cp utils/* /usr/lib/python2.7/site-packages/ansible/module_utils/
    # mkdir /usr/lib/python2.7/site-packages/ansible/modules/storage/dellemc/
    # cd /powermax/library
    # ls
    # cp * /usr/lib/python2.7/site-packages/ansible/modules/storage/dellemc/

    You’ll get an error in case of dellemc directory already exists, which you can ignore.

    At this point, we are ready with an Ansible server with DellEMC PowerMax modules installed.

    There are multiple files in the downloaded directory, each for different management tasks of DellEMC PowerMax (SRP, Volumes, Masking, etc.). We’ll discuss each module in the next blog post in this series.

  • Ansible with DellEMC Storage: Part 2 – Understanding Ansible

    Ansible with DellEMC Storage: Part 2 – Understanding Ansible

    This blog is the continuation of Ansible with DellEMC storage series. Earlier we discussed about getting started with installation of dependencies for Ansible and DellEMC Ansible module, followed by Ansible installation.

    In this blog let’s talk more around Ansible architecture and it’s concepts. So let’ get started.

    Similar to any other platform or software Ansible also has it’s own concepts which you should understand. This will help you get better hands-on with Ansible.

    Below diagram is the high level depiction of the Ansible concepts.

    Ansible Concepts

    On high level there are two types of nodes

    Managed Nodes (Right side of the diagram) – Managed nodes are the devices or software you’ll manage using Ansible. Note that managed nodes don’t need Ansible installed.

    Control/Master Node (Left side of the diagram) – This the machine Ansible is installed. On which you’ll login to run Ansible commands.

    Master node as multiple components which work together. Below are the high level details

    1. Inventory – This is the list of managed nodes which Ansible will talk to. Ansible always refers to node details from inventory file for executing any tasks. Inventory file support grouping, nesting, etc. which makes it easier for management and administration
    2. Modules – Each module defines certain Ansible function. You can execute modules using defining multiple tasks as part of playbooks
    3. Ansible Config – Consider this file as database of Ansible environment variables. Variables set in Ansible config supersedes any other setting configured in Ansible. Usually default configurations in this file are enough for many environments but there will be situations where you need to edit this file (/etc/ansible/ansible.cfg).
    4. Playbooks – Consider playbooks as list of many tasks which Ansible will execute in the sequence. Playbooks are written in YAML (.yml) and hence they are very easy to create and manage without the extensive knowledge of the coding.

    To simplify the playbook understanding just remember that

    • Playbooks contains Plays
      • Plays contains Tasks
        • Tasks call Modules

    Below is the example of Ansible Playbook

    sample Ansible playbook

    There are more concepts when it comes to Ansible (like Tower, Vault, Variables, etc.) but in my personal experience this is the good starting point.

    If you find this information stimulating enough and you want to read further then I would highly recommend that you start from here.

    I hope these bite sized blogs are helping you pickup Ansible faster. More to come šŸ™‚

  • Ansible with DellEMC Storage: Part 1 – Installing Ansible

    Ansible with DellEMC Storage: Part 1 – Installing Ansible

    There are many blogs which cover what is Ansible and why we should care. But this multi-part blog series will cover how DellEMC and Ansible can help you automate many storage tasks.

    Ansible is being used in many organizations nowadays to manage a vast range of infrastructure, ranging from traditional configuration management to cloud resources in public clouds to physical infrastructure such as network and storage devices. There are multiple reasons why you might want to use Ansible, including – but not limited to – below examples.

    • You’re trying to have efficient DevOps environment
    • Automate Day 1/2 tasks
    • Need centralized configuration management

    Getting Started with Ansible

    Even if you’ve not installed Ansible before, it’s very easy to get started. There are many different ways to install Ansible and many dependencies will be needed based on your environment and systems you’ll be managing.

    Once your Linux machine is up and running (CentOS in my case) you can follow next steps

    Apart from Ansible itself there will be many dependencies which needs to be installed. In the case of DellEMC PowerMax storage we will need

    Note that Ansible relies on Python and the Ansible for PowerMax modules relies on a the PyU4V Python library

    So let’s get started

    Check the installed Python version by running below command and make sure it’s supported version

    # python -V

    For installing PIP package on CentOS you will need to install EPEL repository, which can be done by running below command

    # sudo yum install epel-release -y

    Once EPEL is installed you can run below command to install PIP. Also check version once installed

    # sudo yum install python-pip -y
    # pip -V

    As mentioned earlier DellEMC PowerMax Ansible integration relies on a the PyU4V Python library Run below command to install PyU4V

    # pip install PyU4V

    Finally run below command to install Ansible

    # sudo yum install ansible

    At this point you have successfully installed Ansible and ready for next parts.

  • Ansible Master – Enabling SSH Key Based Authentication

    Ansible Master – Enabling SSH Key Based Authentication

    This section seems pretty straight-forward but is the must for all the Ansible deployments.

    Follow below steps to get through the password maze in Ansible environments

    Firstly we will need to generate the SSH authentication keys. This needs to be done on the server from which you want to login to other hosts. In my case it’s Ansible master server.

    Generate your key – Run the ssh-keygen command (as below). By default system will create and store the SSH key into /root/.ssh/id_rsa, which you can change. Passphrase is optional and you can leave it blank.

    Note that if you already have generated the SSH key you have option to overwrite the same, but make sure that earlier key is not used anywhere for authentication. Below example shows option to replace existing SSH keys

    [root@ansible-master ~]# ssh-keygen
    Generating public/private rsa key pair.
    Enter file in which to save the key (/root/.ssh/id_rsa):
    /root/.ssh/id_rsa already exists.
    Overwrite (y/n)? y
    Enter passphrase (empty for no passphrase):
    Enter same passphrase again:
    Your identification has been saved in /root/.ssh/id_rsa.
    Your public key has been saved in /root/.ssh/id_rsa.pub.
    The key fingerprint is:
    SHA256:D52Rvc2F7JMlbikpj7G96Ys3bSLRUz4tNmsfNP4E2Vg root@ansible-master
    The key's randomart image is:
    +---[RSA 2048]----+
    |                 |
    |           o . . |
    |          o . + E|
    |         . o B.@ |
    |        S =.+o&+.|
    |         o.BooOoo|
    |          +.o+ B.|
    |          ..+o=.o|
    |          .+=* .o|
    +----[SHA256]-----+
    

    If you want to use existing keys then you can simply read the existing key which is saved in the file. Below is the example of the reading existing public key

    [root@ansible-master ~]# cat /root/.ssh/id_rsa.pub
    ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAABAQDDoN5+wFiV3Nold4Y7KDGkvIGBqulvdDxDm3qPj7SGsHsnEZKKxbQtO2QJNDJW2tXhLLDxY7vnyQ3xiL0bXbUTkeHHANFY7yZnMH4LH1k51yAkgDdVzKYUdvVJ81qRmYaJUJnLCsKvZMFmg7/KzecuA1QU8WVDLCH02HiRsmqVPaykcR2EOKCgX7i92Q/khZycR66GvoKcVwU9LuDLlADQt9GTaFDFiXPITNayvXkWvL7bwe9arqMCJzmEpvveglJI+vLvh5793yxrszTScTuMpjvpp4Nz5Tk0NSvQqo73yiHAsFF6M7l2hnVskyj3cAOL1dzxmopC/E1qd3DrWSOX root@ansible-master
    

    Once you have generated the SSH key next step is to add the key into target system.

    For copying the SSH keys into target system simply follow below process.

    [root@ansible-master ~]# ssh-copy-id root@192.168.1.101
    /usr/bin/ssh-copy-id: INFO: Source of key(s) to be installed: "/root/.ssh/id_rsa.pub"
    The authenticity of host '192.168.1.101 (192.168.1.101)' can't be established.
    ECDSA key fingerprint is SHA256:qnOPcE09JqKALwLLaL+SqNMy2oubvhF/EevGCcK9S9A.
    ECDSA key fingerprint is MD5:4d:65:b7:e0:e8:09:41:a8:f9:4c:2d:b6:47:55:b2:09.
    Are you sure you want to continue connecting (yes/no)? yes
    /usr/bin/ssh-copy-id: INFO: attempting to log in with the new key(s), to filter out any that are already installed
    /usr/bin/ssh-copy-id: INFO: 1 key(s) remain to be installed -- if you are prompted now it is to install the new keys
    root@192.168.1.101's password:
    
    Number of key(s) added: 1
    
    Now try logging into the machine, with:   "ssh 'root@192.168.1.101'"
    and check to make sure that only the key(s) you wanted were added.
    

    You’ll notice in the command output that this process has added the key into the target system. Note that 192.168.1.101 in above example is target system in which I wanted Ansible master to login without username and password.

    Once the SSH keys are added into the target system now you can try SSH into the target system and it won’t ask for password anymore.

    [root@ansible-master ~]# ssh root@192.168.1.101
    Last login: Tue Nov 26 09:01:16 2019 from gateway
    [root@target-system ~]#
    

    Hope this saves time for many of us.

  • Fix Error – ImportError: No module named packages.urllib3.exceptions

    Fix Error – ImportError: No module named packages.urllib3.exceptions

    Recently when I was creating Python automation script I faced this weird error. This literally wasted my couple of days and needless to mentioned frustration it caused.

    Below is the error message which I was getting

    *
    fatal: [127.0.0.1]: FAILED! => {"changed": true
     "cmd": "python CreateFileSystem.py i-06a848f20bafd0475 10G"
     "delta": "0:00:00.077332"
     "end": "2019-11-21 06:58:53.018383"
     "msg": "non-zero return code"
     "rc": 1
     "start": "2019-11-21 06:58:52.941051"
     "stderr": "CreateFileSystem.py:49: SyntaxWarning: name 'unity_headers' is used prior to global declaration\n  global unity_headers\nTraceback (most recent call last):\n  File \"CreateFileSystem.py\"
     line 5
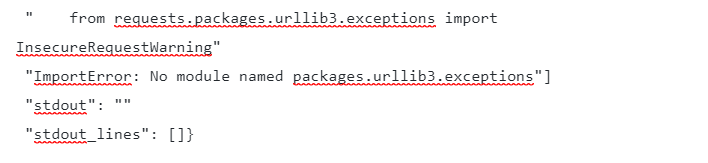
     in <module>\n    from requests.packages.urllib3.exceptions import InsecureRequestWarning\nImportError: No module named packages.urllib3.exceptions"
     "stderr_lines": ["CreateFileSystem.py:49: SyntaxWarning: name 'unity_headers' is used prior to global declaration"
     "  global unity_headers"
     "Traceback (most recent call last):"
     "  File \"CreateFileSystem.py\"
     line 5
     in <module>"
     "    from requests.packages.urllib3.exceptions import InsecureRequestWarning"
     "ImportError: No module named packages.urllib3.exceptions"]
     "stdout": ""
     "stdout_lines": []}

    As you can see from the error it keeps saying that there’s error importing “urllib3” package. But This was already installed in the system

    For resolving this I had to follow below steps.

    • Uninstall below packages
      • python-devel
      • libevent-devel
      • openssl-devel
      • libffi-devel
      • Requests (pip)
      • urllib3 (pip)
    • Install below packages
      • python-devel
      • libevent-devel
      • openssl-devel
      • libffi-devel
    • Run below command
    pip install requests urllib3

    These steps resolved the issue I was facing.

    Also, DO NOT install pip packges (requests and urllib3) individually, run them as single command. This makes sure that required pip dependencies are also auto installed. Strangely I haven’t seen dependencies getting installed when you install them one by one.